

Identity has become one of the most important security boundaries for modern businesses.
Employees work remotely. Customers access cloud applications. Vendors connect to business systems. Teams use SaaS platforms, mobile devices, APIs, and enterprise applications across multiple locations.
As technology environments become more distributed, protecting the network perimeter alone is no longer enough.
Businesses also need to protect who can access systems, what they can access, when they can access it, and whether that access should continue.
This is where enterprise identity security becomes critical.
Enterprise identity security is not simply about creating usernames and passwords. It involves multiple layers of authentication, authorization, monitoring, device security, privileged access controls, and user awareness working together.
A strong identity security strategy can help businesses reduce unauthorized access, limit credential-based attacks, protect sensitive information, and create better control over digital identities.
Here are the six layers businesses should consider when building enterprise identity security.
What Is Enterprise Identity Security?
Enterprise identity security is the collection of policies, technologies, processes, and controls used to protect digital identities and manage access to business systems and information.
It covers identities such as:
- Employees
- Administrators
- Contractors
- Customers
- Vendors
- Partners
- Service accounts
- Applications
- Automated systems
The objective is simple:
Make sure the right identity gets the right access at the right time – and nothing more.
This becomes increasingly important as organizations adopt cloud platforms, remote work, enterprise applications, AI tools, and interconnected systems.
Why Identity Has Become a Major Security Concern
Traditional security models often focused heavily on protecting the network perimeter.
But modern businesses have many users and systems operating outside traditional office environments.
An employee may access:
- Microsoft 365
- CRM systems
- ERP platforms
- Cloud infrastructure
- HR applications
- Collaboration tools
- Business databases
- Customer portals
A compromised identity can potentially provide an attacker with legitimate-looking access to several of these systems.
ParamInfo recent cybersecurity guidance identifies identity-based attacks and credential compromise as major enterprise concerns, including phishing, MFA fatigue, session-token attacks, and other techniques targeting user access.
That is why identity needs to become a core part of the cybersecurity strategy rather than an isolated IT function.
The 6 Layers of Enterprise Identity Security
Layer 1: Identity Governance and Access Management
The first layer is understanding who has access to what.
Identity and Access Management, commonly known as IAM, provides the foundation for managing user identities and permissions.
An effective IAM strategy should answer questions such as:
- Who is this user?
- What department do they belong to?
- What applications do they need?
- What information can they access?
- Who approved their access?
- When should their access expire?
- What happens when they change roles?
- What happens when they leave the organization?
Without effective identity governance, businesses can accumulate unnecessary permissions over time.
For example, an employee may move from finance to another department but continue retaining access to financial systems.
This creates unnecessary risk.
Key IAM controls include:
- User provisioning
- User deprovisioning
- Role-based access
- Access reviews
- Identity lifecycle management
- Authentication policies
- Authorization controls
The goal is to make access structured, controlled, and auditable.
Layer 2: Strong Authentication and MFA
A username and password alone may not provide enough protection for sensitive business systems.
Multi-factor authentication, or MFA, adds additional verification before access is granted.
Authentication can involve multiple factors such as:
- Something the user knows
- Something the user has
- Something the user is
For example, a user may enter a password and then verify their identity using a security key, authenticator application, or biometric method.
MFA can make stolen passwords less useful to attackers because possessing the password alone may not be enough to complete authentication.
Businesses should prioritize stronger authentication for:
- Administrators
- Remote users
- Cloud platforms
- Financial systems
- Sensitive databases
- VPN access
- Business-critical applications
Where appropriate, organizations can also consider phishing-resistant authentication methods such as passkeys or security keys.
Layer 3: Least Privilege and Privileged Access
The third layer is controlling how much access an identity actually receives.
The principle of least privilege means users should receive only the permissions required to perform their responsibilities.
For example, an employee who only needs to view financial reports should not automatically receive permission to modify financial records.
Similarly, a developer may need access to development environments without requiring unrestricted access to production systems.
This is particularly important for privileged accounts.
Administrator accounts can have extensive control over systems, applications, and data.
Businesses should therefore consider:
- Separate administrator accounts
- Privileged access management
- Just-in-time access
- Approval workflows
- Temporary elevated privileges
- Privileged activity monitoring
- Regular access reviews
Reducing unnecessary privileges can limit the potential impact of a compromised account.
Layer 4: Device and Endpoint Identity
A user identity is only part of the access decision.
The device being used to access the system also matters.
Consider two login attempts using the same employee credentials.
One comes from a managed company laptop with current security patches.
The other comes from an unknown device showing suspicious behavior.
Should both receive identical access?
A mature identity security strategy considers device context alongside user identity.
ParamInfo Cybersecurity Services include endpoint security capabilities such as endpoint detection and response, device encryption, antivirus and anti-malware protection, and automated patch management.
Businesses can combine identity and endpoint controls to evaluate:
- Device ownership
- Device health
- Security patch status
- Encryption
- Endpoint protection
- Location
- Login behavior
- Risk indicators
This creates stronger context around each access request.
Layer 5: Zero Trust and Continuous Verification
Traditional security models often assume that users inside a trusted network can be trusted.
Zero Trust takes a different approach.
The principle is often summarized as:
Never trust automatically. Verify continuously.
A Zero Trust approach does not treat network location as sufficient proof of trust.
Instead, access decisions can consider:
- User identity
- Device status
- Application
- Resource sensitivity
- Location
- Risk level
- Authentication strength
- User behavior
For example, an employee accessing a low-risk application from a managed device may receive normal access.
The same employee attempting to access sensitive information from an unfamiliar device may face additional verification or restrictions.
This approach becomes increasingly useful as organizations adopt cloud applications and remote working models.
ParamInfo Cloud Migration Checklist for UAE Businesses in 2026 specifically highlights access reviews and Zero Trust security principles as part of secure cloud operations.
Zero Trust should not be treated as a single product.
It is a security model that brings identity, devices, applications, networks, data, and monitoring together.
Layer 6: Monitoring, Detection, and User Awareness
Even strong identity controls need continuous monitoring.
Businesses should be able to identify unusual identity activity.
Examples include:
- Multiple failed login attempts
- Unusual login locations
- Impossible travel patterns
- Repeated MFA requests
- New device registrations
- Privilege changes
- Unusual access to sensitive information
- After-hours administrative activity
- Sudden changes in account behavior
Monitoring can help security teams identify potentially compromised accounts and investigate suspicious activity.
But technology is only part of the solution.
Users also need to understand identity-related threats.
Employees should be trained to recognize:
- Phishing
- Credential theft
- MFA fatigue attacks
- Social engineering
- Suspicious password-reset requests
- Impersonation attempts
- Unexpected access requests
ParamInfo article on Vishing Attacks and IT Help Desk Security explains how attackers can impersonate employees or vendors to manipulate help-desk personnel into resetting credentials or granting access.
This demonstrates an important point:
Identity security is not only a technology problem. It is also a people and process problem.
How the Six Layers Work Together
The six layers should not operate independently.
Consider a user attempting to access a sensitive business application.
Step 1: Identity
The organization identifies the user.
Step 2: Authentication
The user proves their identity using appropriate authentication controls.
Step 3: Authorization
The system determines what the user is allowed to access.
Step 4: Device
The security system evaluates whether the device meets required security conditions.
Step 5: Zero Trust
Additional context and risk signals are evaluated before access is granted.
Step 6: Monitoring
The access event is logged and monitored for unusual behavior.
This creates a layered defense rather than relying on a single security control.
Why Businesses Should Avoid Relying on Passwords Alone
Passwords remain widely used, but they can be exposed through:
- Phishing
- Credential stuffing
- Password reuse
- Malware
- Social engineering
- Data breaches
- Keylogging
Even strong passwords can eventually be compromised.
That is why enterprise identity security should combine passwords with additional controls such as MFA, device verification, access policies, monitoring, and user awareness.
The objective is not to make authentication unnecessarily complicated.
It is to make unauthorized access significantly harder while keeping legitimate access practical.
Identity Security in Cloud Environments
Cloud adoption changes how identity needs to be managed.
Instead of accessing applications only from corporate offices, employees may connect from homes, airports, customer sites, or mobile devices.
Cloud environments may also contain:
- Multiple SaaS applications
- Cloud infrastructure
- APIs
- Service accounts
- Third-party integrations
- Remote administrators
- Automated workloads
This makes identity governance increasingly important.
Businesses should regularly review cloud permissions and remove access that is no longer required.
For enterprise AI and knowledge systems, access controls are also important at the data level.
Identity Security for Employees, Contractors, and Vendors
Businesses should not focus only on permanent employees.
External identities can also create security risks.
Contractors, consultants, vendors, and partners may require access to business systems.
Their access should have:
- Clear ownership
- Defined permissions
- Expiration dates
- Approval requirements
- Monitoring
- Periodic reviews
When the relationship ends, access should be removed promptly.
This is particularly important for organizations that work with multiple external technology providers.
What Happens When an Employee Leaves?
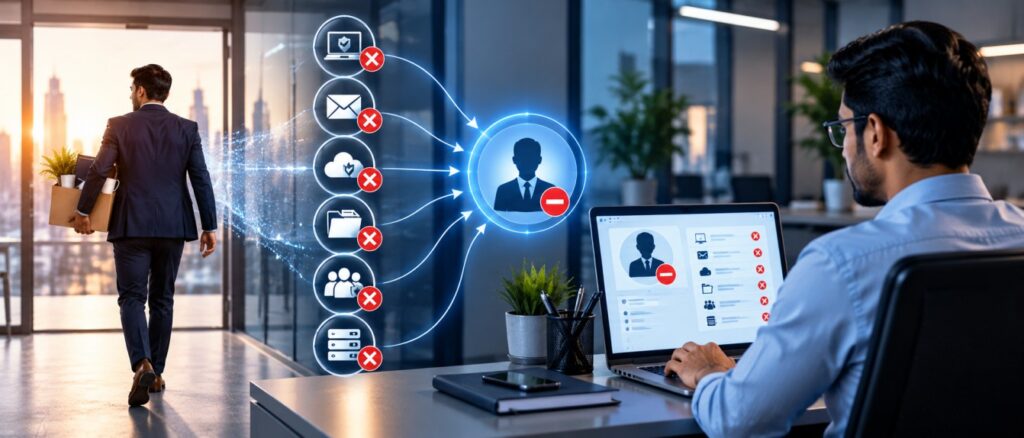
Offboarding is a critical identity security process.
A strong offboarding process should coordinate:
- HR notification
- Account deactivation
- Application access removal
- VPN access removal
- Privileged access removal
- Device recovery
- Token and session revocation
- Shared credential review
- Data access review
- Third-party access review
The faster and more consistently this process happens, the lower the risk of former users retaining unnecessary access.
How Businesses Can Improve Enterprise Identity Security
Businesses do not need to implement every security control simultaneously.
A practical approach is to start with the fundamentals.
Step 1: Inventory Identities
Identify employees, contractors, vendors, service accounts, applications, and privileged accounts.
Step 2: Review Existing Permissions
Determine whether users have more access than their roles require.
Step 3: Strengthen Authentication
Implement MFA and stronger authentication for critical systems.
Step 4: Protect Privileged Accounts
Separate administrative access and monitor privileged activity.
Step 5: Evaluate Devices
Make device security part of access decisions.
Step 6: Introduce Zero Trust Principles
Move away from implicit trust and evaluate access based on identity, device, resource, and risk.
Step 7: Monitor Identity Activity
Look for unusual login and access behavior.
Step 8: Train Employees
Make identity security part of the organization’s security culture.
Common Enterprise Identity Security Mistakes
Even organizations with security programs can make identity-related mistakes.
Giving Too Much Access
Employees often accumulate permissions as they move between roles.
Forgetting Service Accounts
Automated systems and applications also have identities that need protection.
Ignoring Third-Party Access
Vendor accounts can become forgotten entry points.
Treating MFA as the Entire Solution
MFA is important, but it is only one layer of identity security.
Failing to Review Permissions
Access should be reviewed periodically rather than granted permanently.
Ignoring Help-Desk Security
Attackers may target support processes to manipulate employees into resetting credentials or granting access.
Not Monitoring Identity Behavior
A strong access policy becomes less effective if suspicious account activity is not detected.
A Simple Enterprise Identity Security Checklist
Use this checklist to assess your current identity security program:
- All user identities are inventoried
- Former employee accounts are disabled promptly
- Contractor and vendor access is reviewed
- MFA protects critical systems
- Privileged accounts are separately managed
- Least-privilege principles are applied
- Device security is considered during access decisions
- Cloud permissions are reviewed regularly
- Identity activity is monitored
- Suspicious authentication events are investigated
- Help-desk identity verification procedures exist
- Employees receive security awareness training
- Access reviews are performed periodically
- Incident response procedures include compromised identities
Enterprise identity security is no longer just about usernames and passwords.
Modern businesses need layered controls that protect identities throughout their entire lifecycle.
The six layers provide a practical framework:
1. Identity Governance and Access Management
2. Strong Authentication and MFA
3. Least Privilege and Privileged Access
4. Device and Endpoint Identity
5. Zero Trust and Continuous Verification
6. Monitoring, Detection, and User Awareness
The strength of the strategy comes from combining these layers.
An attacker who obtains a password should not automatically gain unrestricted access.
A contractor should not retain access after a project ends.
An administrator should not have unlimited privileges simply because they have a privileged account.
And a suspicious login should not look identical to normal business activity.
The objective of enterprise identity security is to create a controlled, continuously monitored environment where legitimate users can access what they need while unnecessary and suspicious access is restricted.
Protect the identity. Control the access. Monitor the activity.
That is the foundation of a stronger modern cybersecurity strategy.
Frequently Asked Questions
1. What is enterprise identity security?
Enterprise identity security is the combination of technologies, policies, and processes used to protect digital identities and control access to business systems, applications, devices, and data.
2. Why is identity security important for businesses?
Compromised credentials can provide attackers with legitimate-looking access to business systems. Strong identity security helps reduce unauthorized access and limits the potential impact of compromised accounts.
3. What are the six layers of enterprise identity security?
The six layers are identity governance and access management, strong authentication and MFA, least privilege and privileged access, device and endpoint identity, Zero Trust and continuous verification, and monitoring, detection, and user awareness.
4. Is MFA enough to protect enterprise identities?
No. MFA is an important security control, but businesses also need access governance, least privilege, device security, monitoring, user awareness, and other layered protections.
5. What is the principle of least privilege?
Least privilege means giving users only the access and permissions required to perform their responsibilities, rather than providing unnecessary or excessive access.
6. What is Zero Trust identity security?
Zero Trust identity security assumes that access should not be automatically trusted based solely on network location. Access decisions can continuously consider identity, device, application, resource, and risk.
7. How does endpoint security support identity security?
Endpoint security helps determine whether devices accessing business systems are protected, updated, encrypted, and showing signs of suspicious activity.
8. Should businesses monitor employee login activity?
Businesses should monitor authentication and access activity in accordance with applicable laws, policies, and legitimate security requirements. Monitoring can help identify suspicious behavior and compromised accounts.
9. How should businesses manage contractor access?
Contractor access should have defined permissions, clear ownership, appropriate approval, monitoring, and expiration or removal when the engagement ends.
10. Why is privileged access important?
Privileged accounts can have extensive control over systems and data. Protecting and monitoring these accounts can reduce the potential impact of credential compromise or misuse.
11. What is identity governance?
Identity governance involves managing who has access to business resources, why they have that access, who approved it, and when the access should be reviewed or removed.
12. How can ParamInfo help with enterprise identity security?
ParamInfo provides cybersecurity capabilities covering areas such as security assessment and audit, network security, endpoint security, data security, and physical security integration. These capabilities can support businesses in building a broader, layered cybersecurity strategy.
